Trust in AI is possible, and the tools to build it are already here.
Advanced AI Society is the alliance for verifiable AI: a new category of AI built on open verification, the foundation for securing and trusting autonomous systems.
Featured at
- Davos
- Linux Foundation Decentralized Trust
- RSA Conference / Polaris Collective
- MIT
- Consensus
- Eve Wealth Summit
- United Nations
- Black Hat
Why it matters
Unverifiable Agent Controls Are an Existential Risk and a Business Liability.
When an agent approves a refund, edits a patient record, moves money between accounts, how do you show what it was actually allowed to do and whether it followed instructions? Today the only answer comes from the system’s logs, which are claims, not evidence. There’s no way to verify or challenge claims-based AI. Learn more →
From claims to evidence
Verifiable AI is a new category of AI that makes trust in AI systems possible
Insurable AI, Sovereign AI, Responsible AI all require Verifiable AI
AI Tomorrow
Claims-based AI asks you to trust agent logs. Verifiable AI produces a separate piece of evidence of what the agent did, which is either attested by an independent verifier or, with open verification, verifiable by anyone without trusting the operator or an auditor.
| Claims-based AIVerifiability Tier 1 · where most AI is today | Verifiable AIFrom Verifiability Tier 2 · at minimum | Verifiable AI with open verificationProof-of-Control Verifiability Tiers 3 and 4 | |
|---|---|---|---|
| Who is the actor? | Inferred from credentials. | Attested. | The actor's identity is bound to a known operator, and anyone can openly verify it. |
| What were they allowed to do? | Asserted in policy. | Authority is documented and signed in policy. | Authority is signed and scoped, and anyone can openly verify each grant. |
| What did they actually do? | Actions reconstructed from logs. | Each action carries evidence. | Each action carries tamper-evident evidence anyone can openly verify. At Verifiability Tier 4, the action cannot run without it. |
| What is the agent made of? | Undocumented, changes silently. | Composition documented and attested. | Composition is fingerprinted, so a swapped model shows up. |
| Who can verify? | Only the vendor. | Someone other than the vendor. | Anyone can openly verify, without trusting the operator or an auditor. |
Verifiable AI
The technology is here. The industry is scattered.
Verifiable AI is a latent category waiting for structural unification.
The technology to verify agentic orchestration already exists across a range of cryptographic and decentralized services: from trusted execution environments and hardware attestation to zero-knowledge proofs.
- Cryptographic Logging
- Hardware Attestation
- Identity Binding
- Trusted Execution
- Verifiable Credentials
- Delegation Chains
- Zero-Knowledge Proofs
- Secure Enclaves
- Digital Signatures
- Merkle Trees
- Post-Quantum Signatures
- Decentralized Identity
- Remote Attestation
- TPM
- Confidential Computing
- Model Signing
- Verifiable Inference
- GPU Attestation
- Agent Identity
- Attestation Tokens
- Multi-Party Computation
- zkML
- Homomorphic Encryption
- Provenance Tracking
- Chain of Custody
- Access Control Logs
- Permission Delegation
- Cryptographic Receipts
- Time-Stamping
- Non-Repudiation
- Verified Compute
- W3C Credentials
- TEE Attestation
- Audit Trails
- SBOM
- Content Credentials
- C2PA
- Runtime Attestation
- Supply-Chain Attestation
- Key Attestation
- Workload Identity
- Transparency Logs
- SLSA Provenance
- Capability Tokens
- Data Lineage
Our founding imperatives
Build the third-party open verification ecosystem
Open verification is a new category of open source: the open standards and specifications that let anyone verify what an AI system did, without trusting the operator or an auditor.
Proof-of-Control is our flagship standard for evidence that an AI agent stayed within the controls it was given. It is one of many ways to achieve open verification.
Electricity earned society’s trust through a similar assurance maturation process: insurers funded the lab that became Underwriters Laboratories in 1894, and the first national electrical code followed three years later.
01 · Build open verification
We need to rebuild AI security and governance for the machine-to-machine era.
Agents now act faster than any person can follow, and point-in-time audits are insufficient. Verification has to be continuous and run at machine speed: embedded natively in agentic infrastructure, built as open-source public architecture no single vendor owns, and independently certifiable.
Build with the Lab →02 · Modernize policy
Verification cannot belong to the verified.
Anyone who relies on an AI system should be able to verify what it did without depending on the operator. That ability needs to be legally enforceable and written into national and state policy, on open standards no single vendor owns.
See how policy can catch up →03 · Adopt verifiable AI
Enterprises that can show what their agents did will be the ones that can deploy faster, be insured, and be trusted.
Claims-based AI cannot keep up with the machine-to-machine era. The pressure to move to verifiable AI is arriving from three sides at once: boards wanting AI adoption without losing control, insurers deciding whether to cover AI, and regulators asking for evidence of what AI did. Enterprises need to expand beyond claims-based AI to verifiable AI that is publicly definable, commercially procurable, and broadly insurable, so they can put agents into production with the evidence needed to secure them.
Join the Consortium →
Our work
Accelerating the market for Verifiable AI
The nonprofit
Build open verification
Open Verification Lab
Builds the open-source, public-goods architecture for open verification at machine speed, making verifiable AI natively embedded and independently certifiable.
Explore the LabModernize policy
Verifiable AI Policy Institute
Educates policymakers to make verifiable AI legally enforceable.
Explore the Policy InstituteThe membership organization
Adopt verifiable AI
Verifiable AI Consortium
Drives adoption of verifiable AI across the market, making it publicly definable, commercially procurable, and broadly insurable.
Explore the ConsortiumWhat's happening
Highlighted event
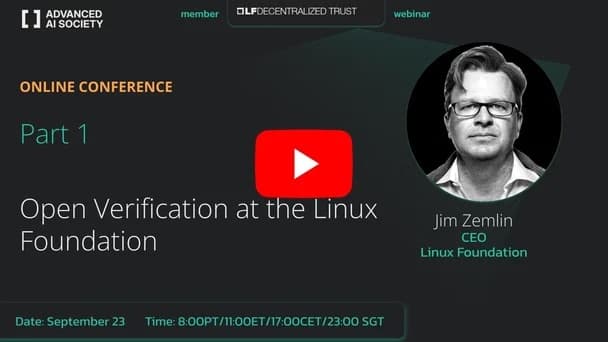
Who’s Watching the Machines? Launching Open Verification, the Proof-of-Control Standard for the Agentic EraOpen Verification at the Linux Foundation, with Jim Zemlin, CEO, Linux Foundation.
Consortium members
See all members →





A listing shows membership. It does not certify a product.
We work alongside
“Since becoming a member, we’ve had new doors open up, starting with our Davos experience.”
Get involved
For organizations
Join the Verifiable AI Consortium
For start-up builders of verifiable AI or enterprises looking to adopt verifiable AI
Member dues fund the category creation work: convenings, analyst-grade research, and industry working groups.
For individuals
Join as a Founding Contributor for Proof-of-Control
For engineering and security executives and practitioners who make decisions on how AI is implemented or purchased, including CIOs, CTOs, CISOs, security practitioners, cryptographers, GRC professionals and AI security researchers.
There is no cost to join.
Google sign-in required